
Blog · Guide · · 4 min read
Two head offices, and each branch uses the nearer one
With a firewall in London and another in Virginia, a branch in Virginia should not reach the internet through London. One setting makes each office use the nearest: a web request went from 0.465 s to 0.040 s, and when the near one failed, traffic moved to the far one within about a minute.
The perimeter guide sent a branch's internet through head office's firewall. Companies with two head offices, one in Europe and one in America say, usually have a firewall at each. Then the question is which one each branch should use, and the answer that makes sense is the nearer one: a branch in Virginia has no business reaching the internet through London.
As always, a real run. Two head offices, each with a firewall set as a Weft perimeter, one in AWS's London region and one in Virginia, and a branch next to each. A PC at each branch asked every ten seconds which address the internet saw it at, and the Virginia one timed each request.
What you need
- Two or more sites each set up as a perimeter, as in the perimeter guide. Each firewall must also route replies for the other offices back through its own Weft box, since any office may now use it.
- Your other offices set up as in the earlier guides. Nothing to set at any of them.
Before: one firewall for everyone
With two perimeters and the standard setting, every site uses the same one, chosen by routing. In our run that was London, for both branches:
London branch     internet sees me at: 18.171.147.146
Virginia branch   internet sees me at: 18.171.147.146 in 0.465 s
Weft measures every tunnel all the time, and Paths showed why the Virginia branch was slow: it is 75 ms from London and less than 1 ms from its own head office. Every connection it made crossed the Atlantic and came back.
A note from this run: the first time through, the standard setting did not choose one firewall at all. It spread each branch's connections across both, so the internet saw the same branch at two addresses on two continents. We fixed that before going on, and "every site uses the same one" is now true.
1. Choose the nearest
Open Settings, find perimeter_policy, choose nearest and press Set.
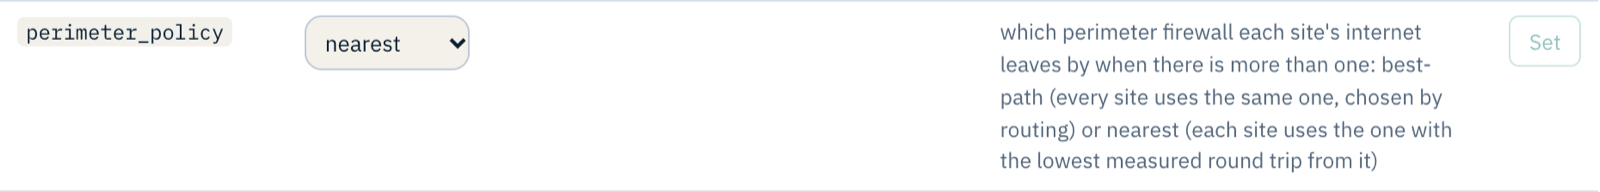
From then on Weft picks, for each site, the perimeter with the lowest measured round trip from that site, and keeps picking as the measurements change. To stop sites switching back and forth between two firewalls at similar distances, a new one has to be clearly nearer before a site moves.
2. Watch the Virginia branch
15:09:35  (Set pressed)
15:09:50  internet sees me at: 18.171.147.146 in 0.465 s
15:10:00  internet sees me at: 44.193.75.253 in 0.040 s
15:10:10  internet sees me at: 44.193.75.253 in 0.036 s
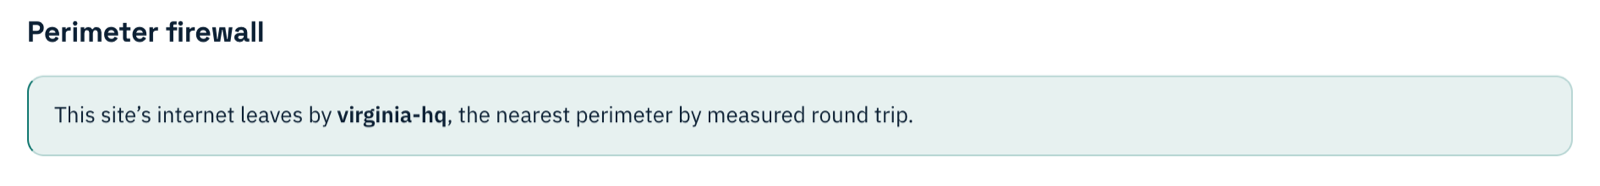
Within 25 seconds the Virginia branch was leaving by Virginia's firewall, and the same small request took less than a tenth of the time: a median of 0.040 s, against 0.465 s through London. The London branch stayed with London throughout. Each site's page now says where its internet leaves, and why:
3. Switch the near one off
We stopped the Virginia head office's Weft box without warning:
15:12:33  (Virginia head office's box stopped)
15:12:47  no answer
15:12:57  internet sees me at: 18.171.147.146 in 0.466 s
One request failed, and 24 seconds after the box stopped the Virginia branch was leaving through London: slower, but online. We ran it a second time and kept the box off for nine minutes: three requests failed and the branch was back online through London after 63 seconds, and stayed there.
When the Virginia box was started again, the branch went back to it by itself, 50 seconds after the start and without a failed request:
16:12:18  (Virginia head office's box started)
16:12:58  internet sees me at: 18.171.147.146 in 0.466 s
16:13:08  internet sees me at: 44.193.75.253 in 0.037 s
That second run is the one to trust. The first time the box came back, the branch did not: the restarted box had lost the route to its own office network, so nothing it was sent ever reached its firewall, while every site reported healthy. We found the cause, the box now repairs it by itself, and the second run above is the fixed version doing exactly that.
If something does not work
| What you see | What it means |
|---|---|
| A site uses the far firewall | Check Paths: the near one may really be further away right now. Weft goes by measurement, not by map. |
| A site's internet stops when it moves to another firewall | That firewall has no route back to the site's network through its own Weft box, or does not accept traffic from it. |
| No "leaves by" line on a site | The organisation has fewer than two perimeters, or perimeter_policy is not set to nearest. |
What you have now
Each office's internet leaving by the firewall nearest to it, chosen from real measurements, and moving to the next one by itself when that firewall's office goes down. Add a third head office with a firewall and the offices near it start using it, with nothing set anywhere else.